Secure Boot Attestation verifies that the device firmware and boot process are authentic and have not been tampered with. This step ensures that the device itself is in a trustworthy state.
Why it matters:
-
Prevents compromised firmware from interacting with the system.
-
Confirms device integrity before performing sensitive operations.
How it works
-
Request Secure Boot Challenge Word (BootCW).
-
Compute and submit the Host Response Word (HRW).
-
Check attestation status — only proceed if
AUTH_OK.
Prerequisites
-
Client must be authenticated.
-
Valid
CF-Access-Client-IDandCF-Access-Client-Secretare required. -
Devices must be ordered correctly in the chain.
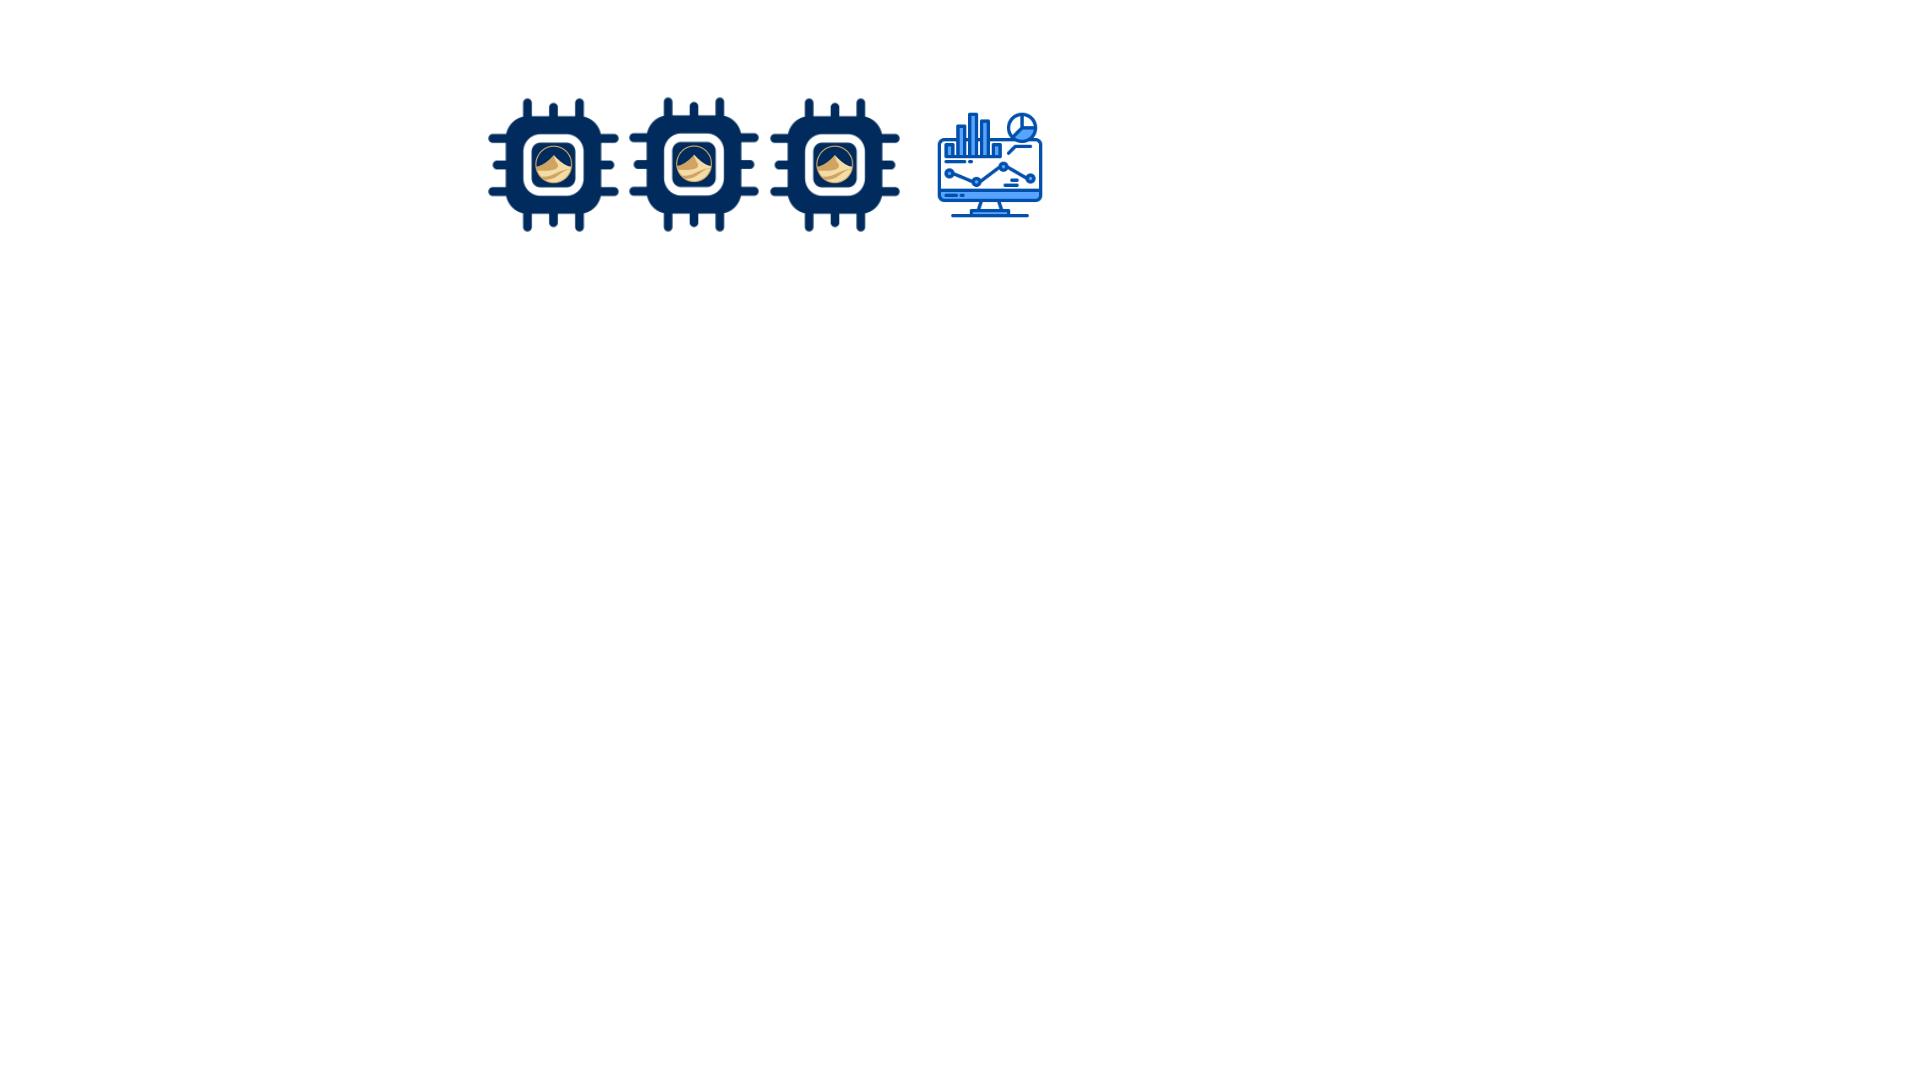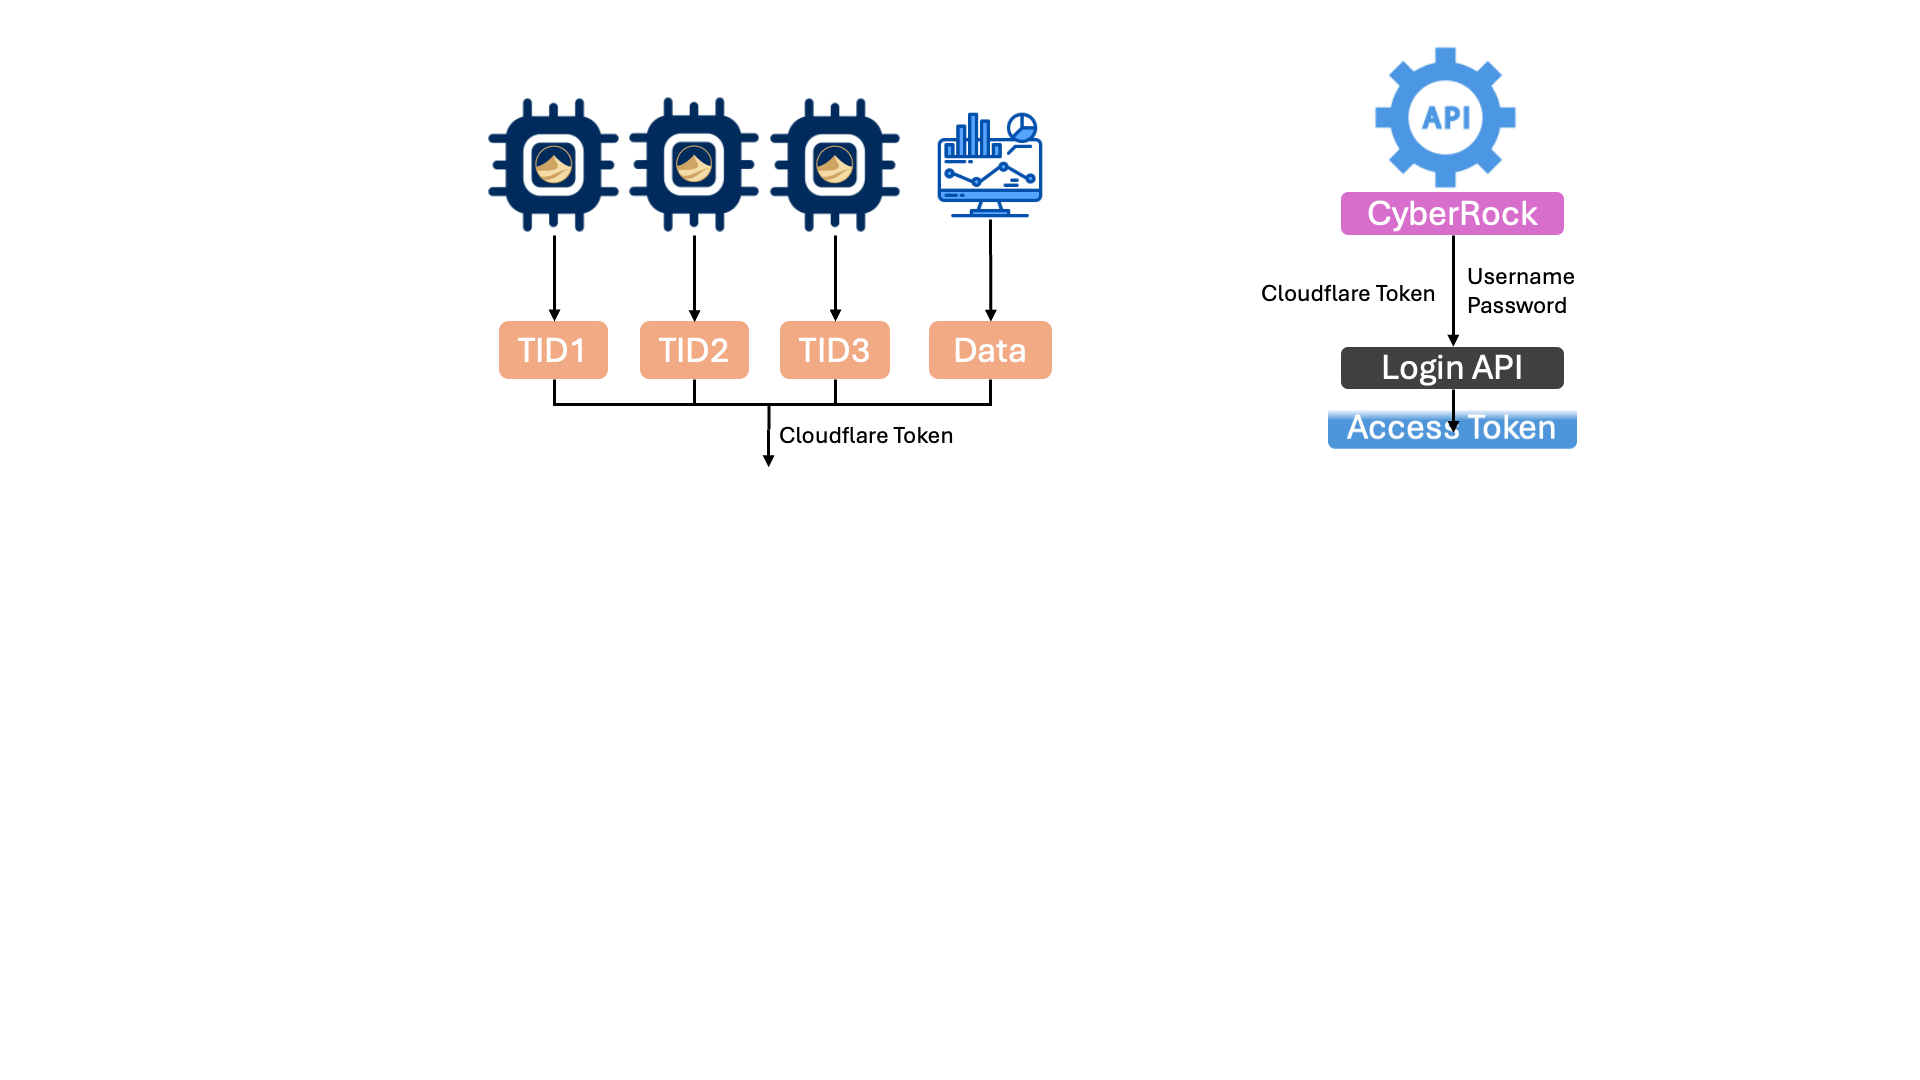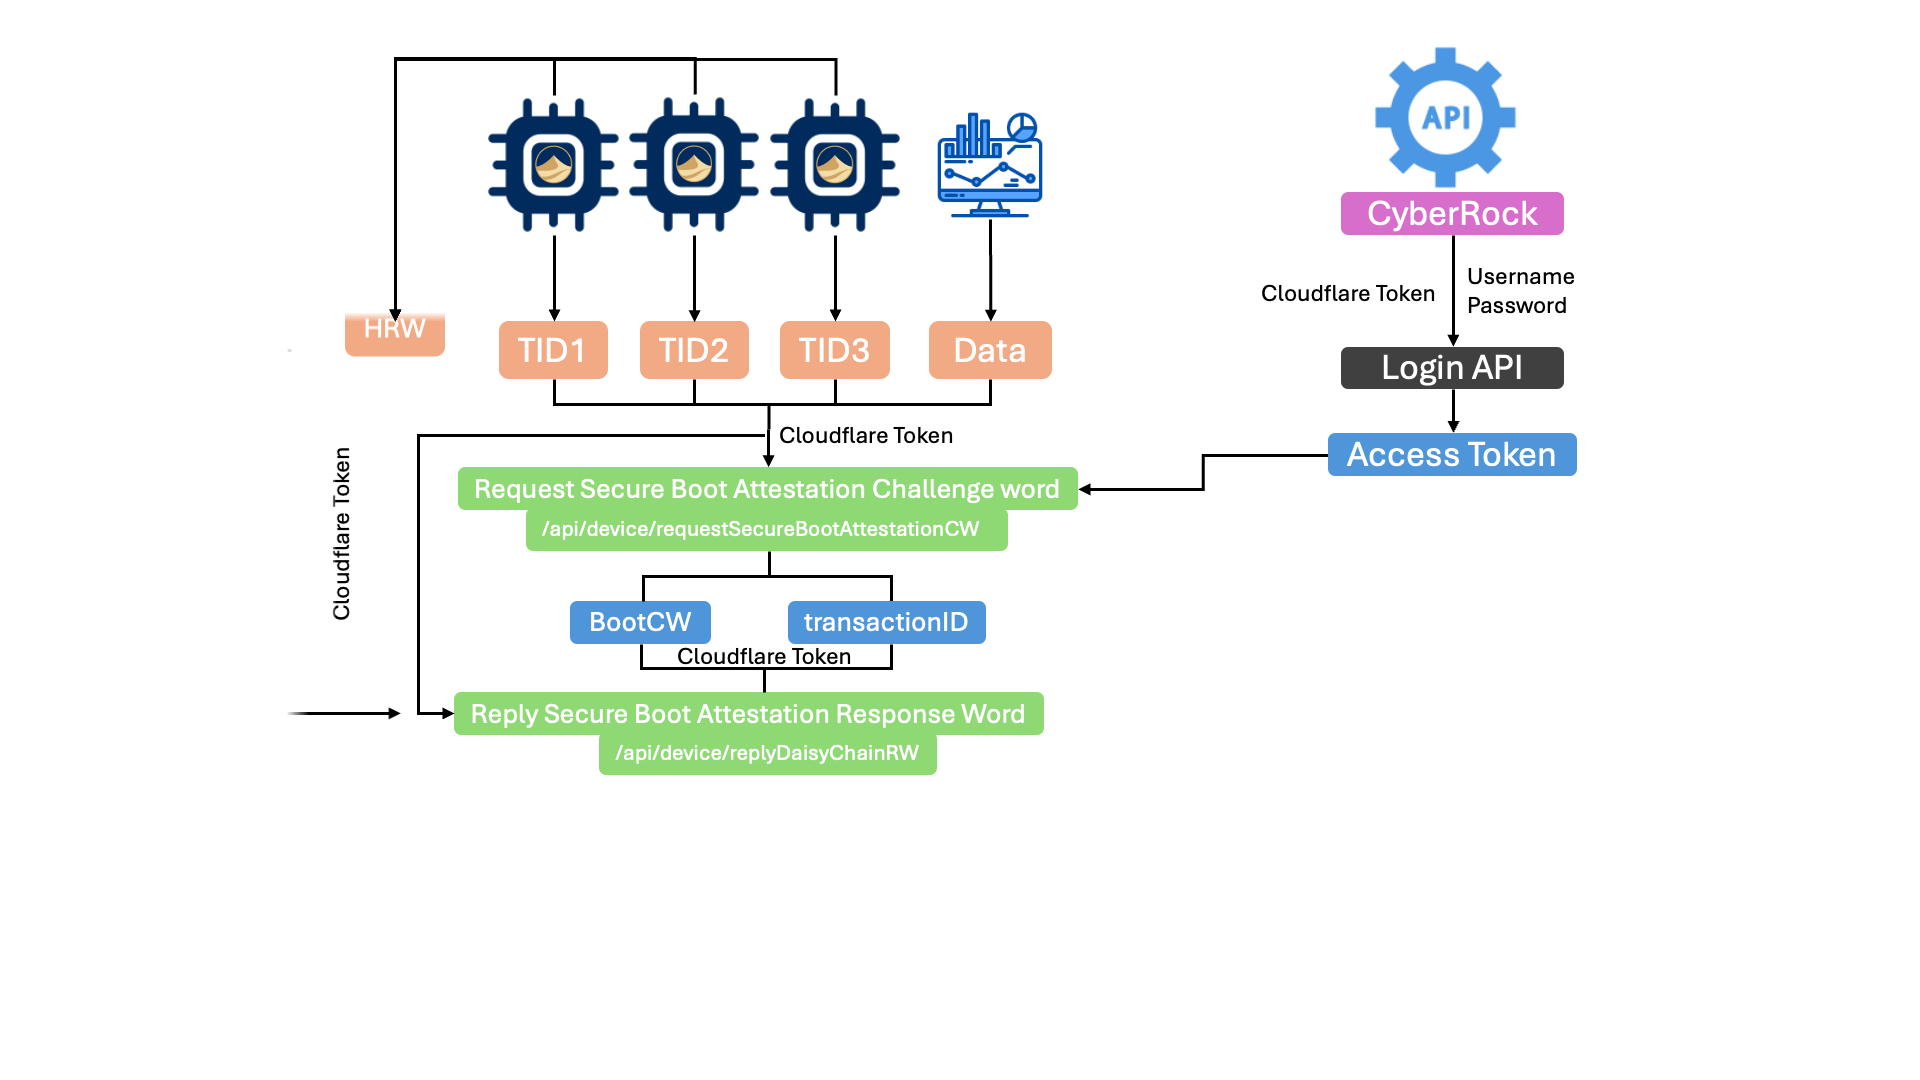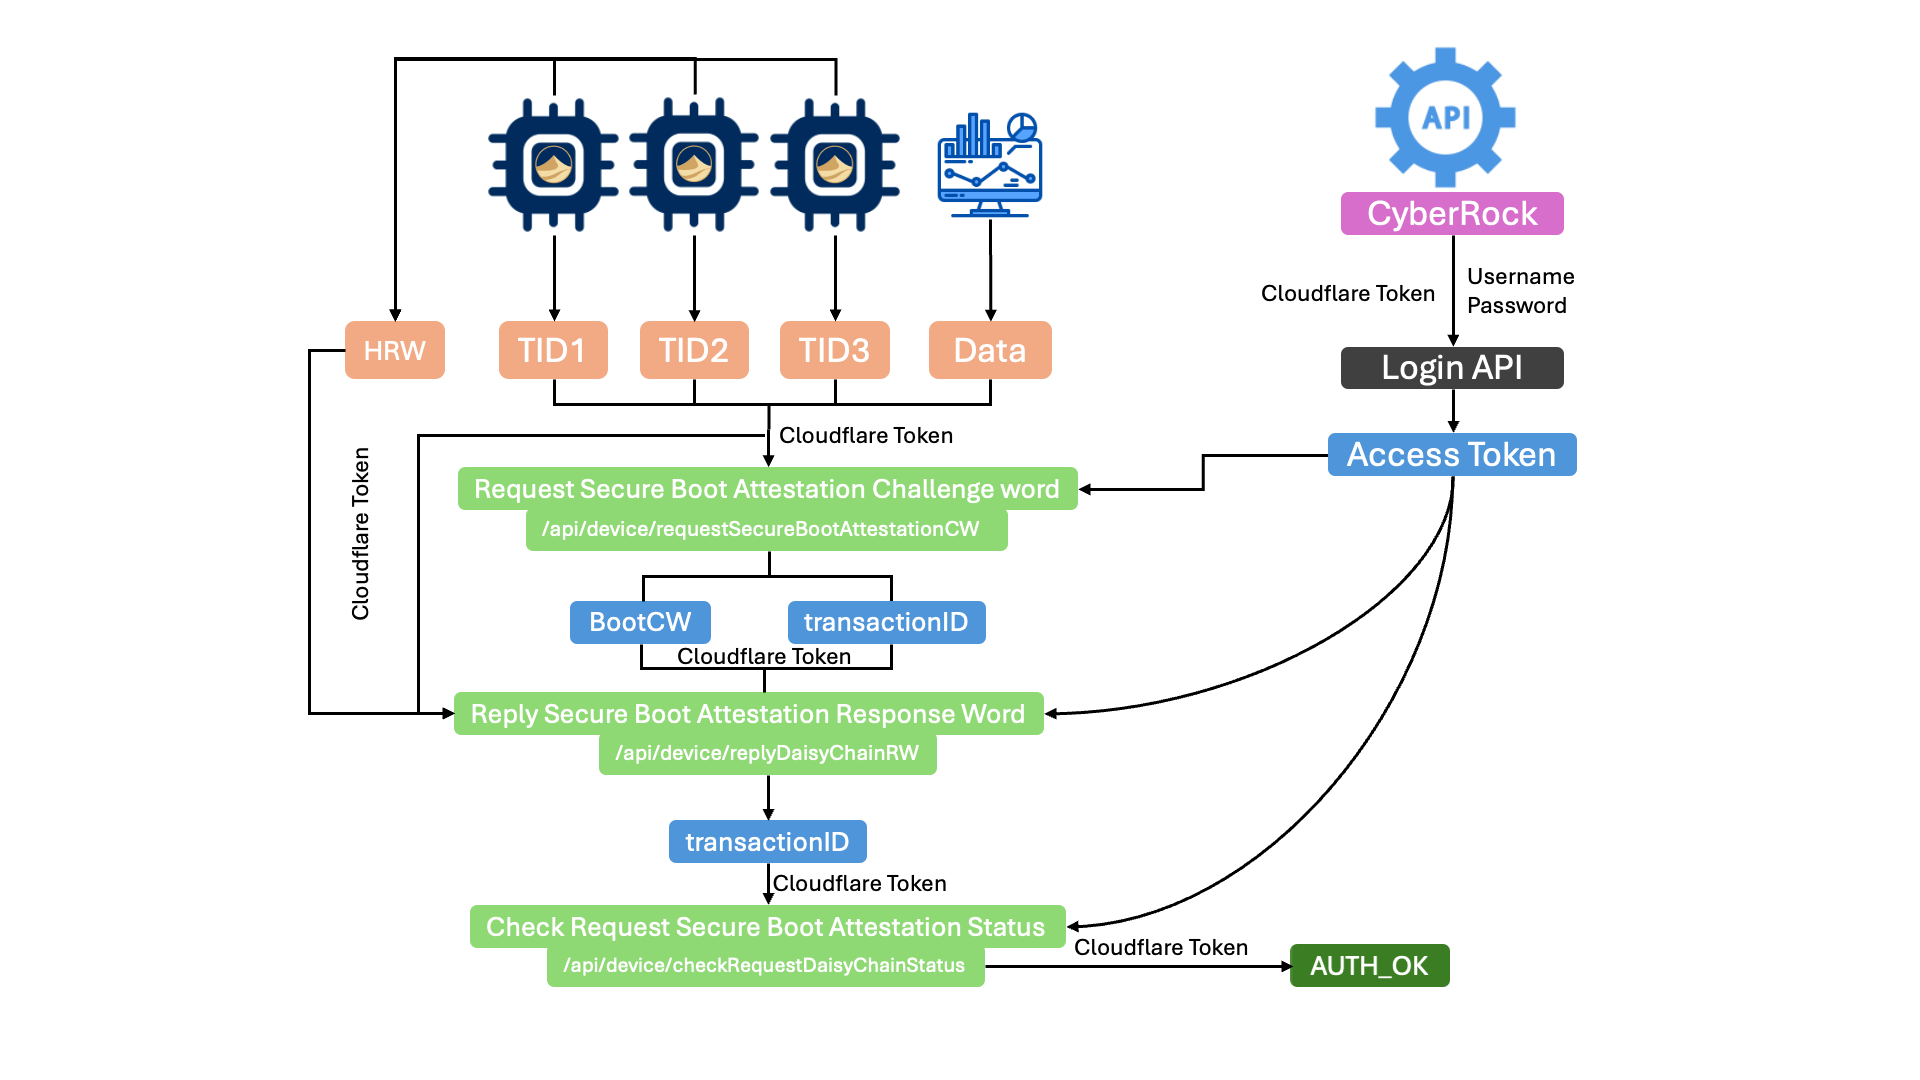
End-to-End Flow
-
Client requests Boot Challenge Word (BootCW)
-
Devices compute the Host Response Word (HRW)
-
Client submits Secure Boot RW
-
Service validates the attestation
-
Client polls status API until final result
| ← Daisy Chain Host Response Word (HRW) | Host Secure Boot Attestation → |