Token Daisy Chain Authentication is a device-level verification step. It confirms that the device can correctly respond to cryptographic challenges, forming the foundation of the authentication process.
Why it matters:
- Ensures that only genuine devices can access the system.
- Prevents unauthorized or rogue devices from entering the network.
- Provides a secure starting point for host verification and subsequent Secure Boot checks.
End-to-End Usage Guide
Token Daisy Chain Authentication validates a sequence of devices in a predefined order. Each device contributes to the authentication chain, ensuring that all devices are genuine and correctly linked before authentication succeeds.
Prerequisites
Before using the Daisy Chain APIs:
- Login using username and password to obtain an access token.
- Include the access token in the
Authorizationheader for all subsequent API calls. - Keep
CF-Access-Client-IDandCF-Access-Client-Secretready. - Ensure you have the ordered list of device TIDs and optional intermediate data.
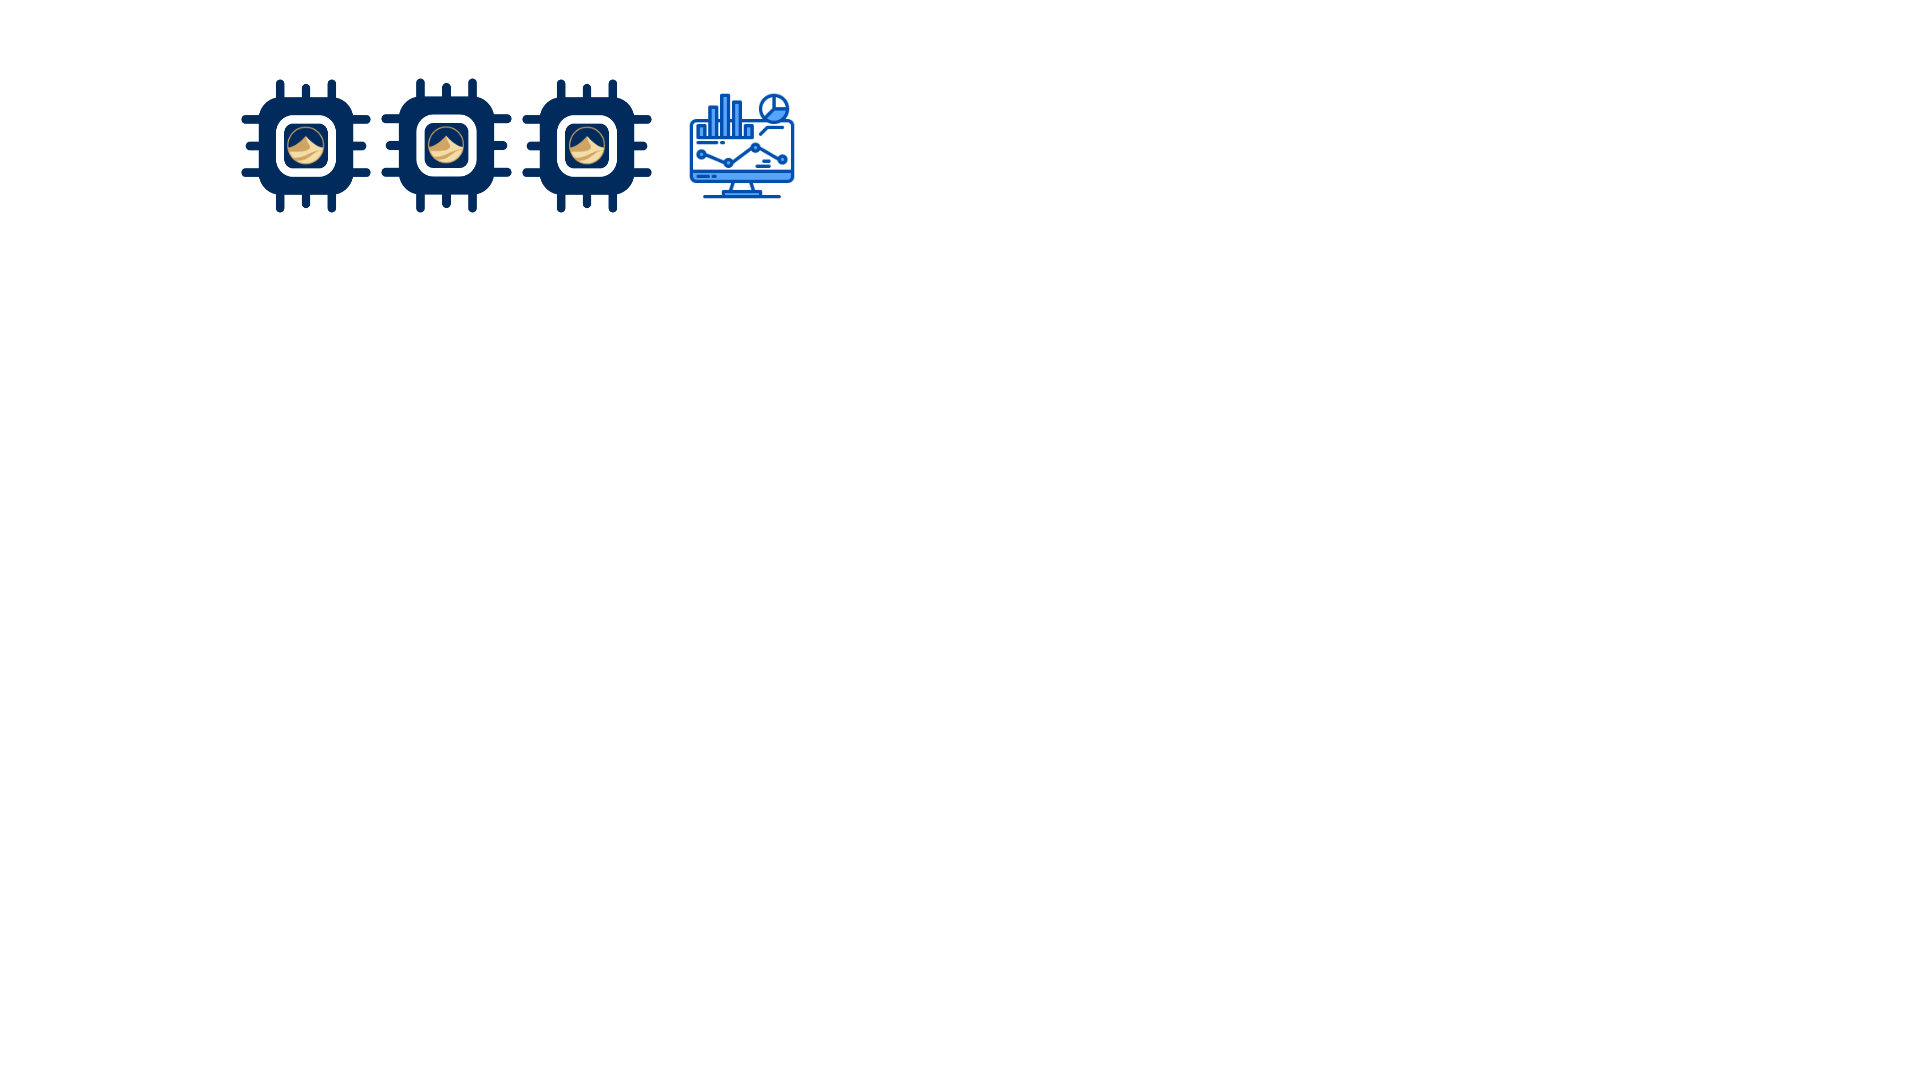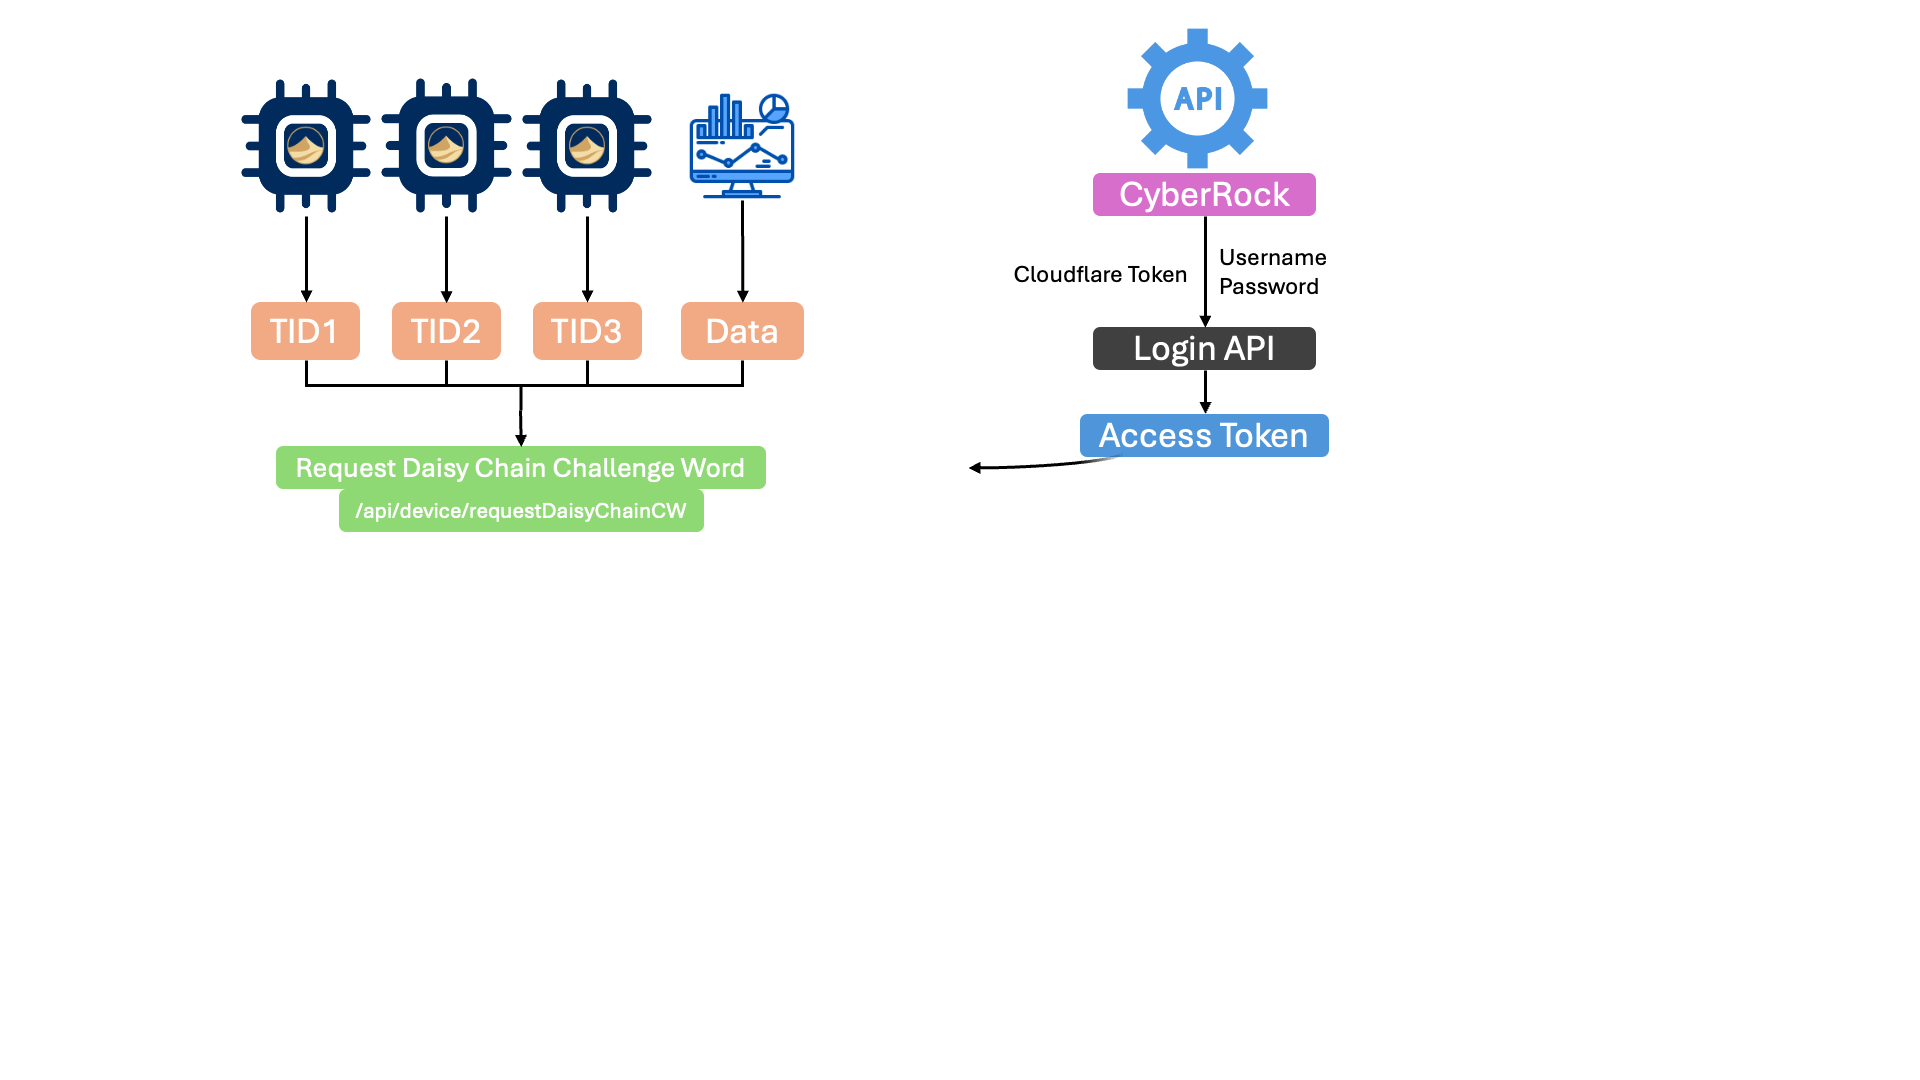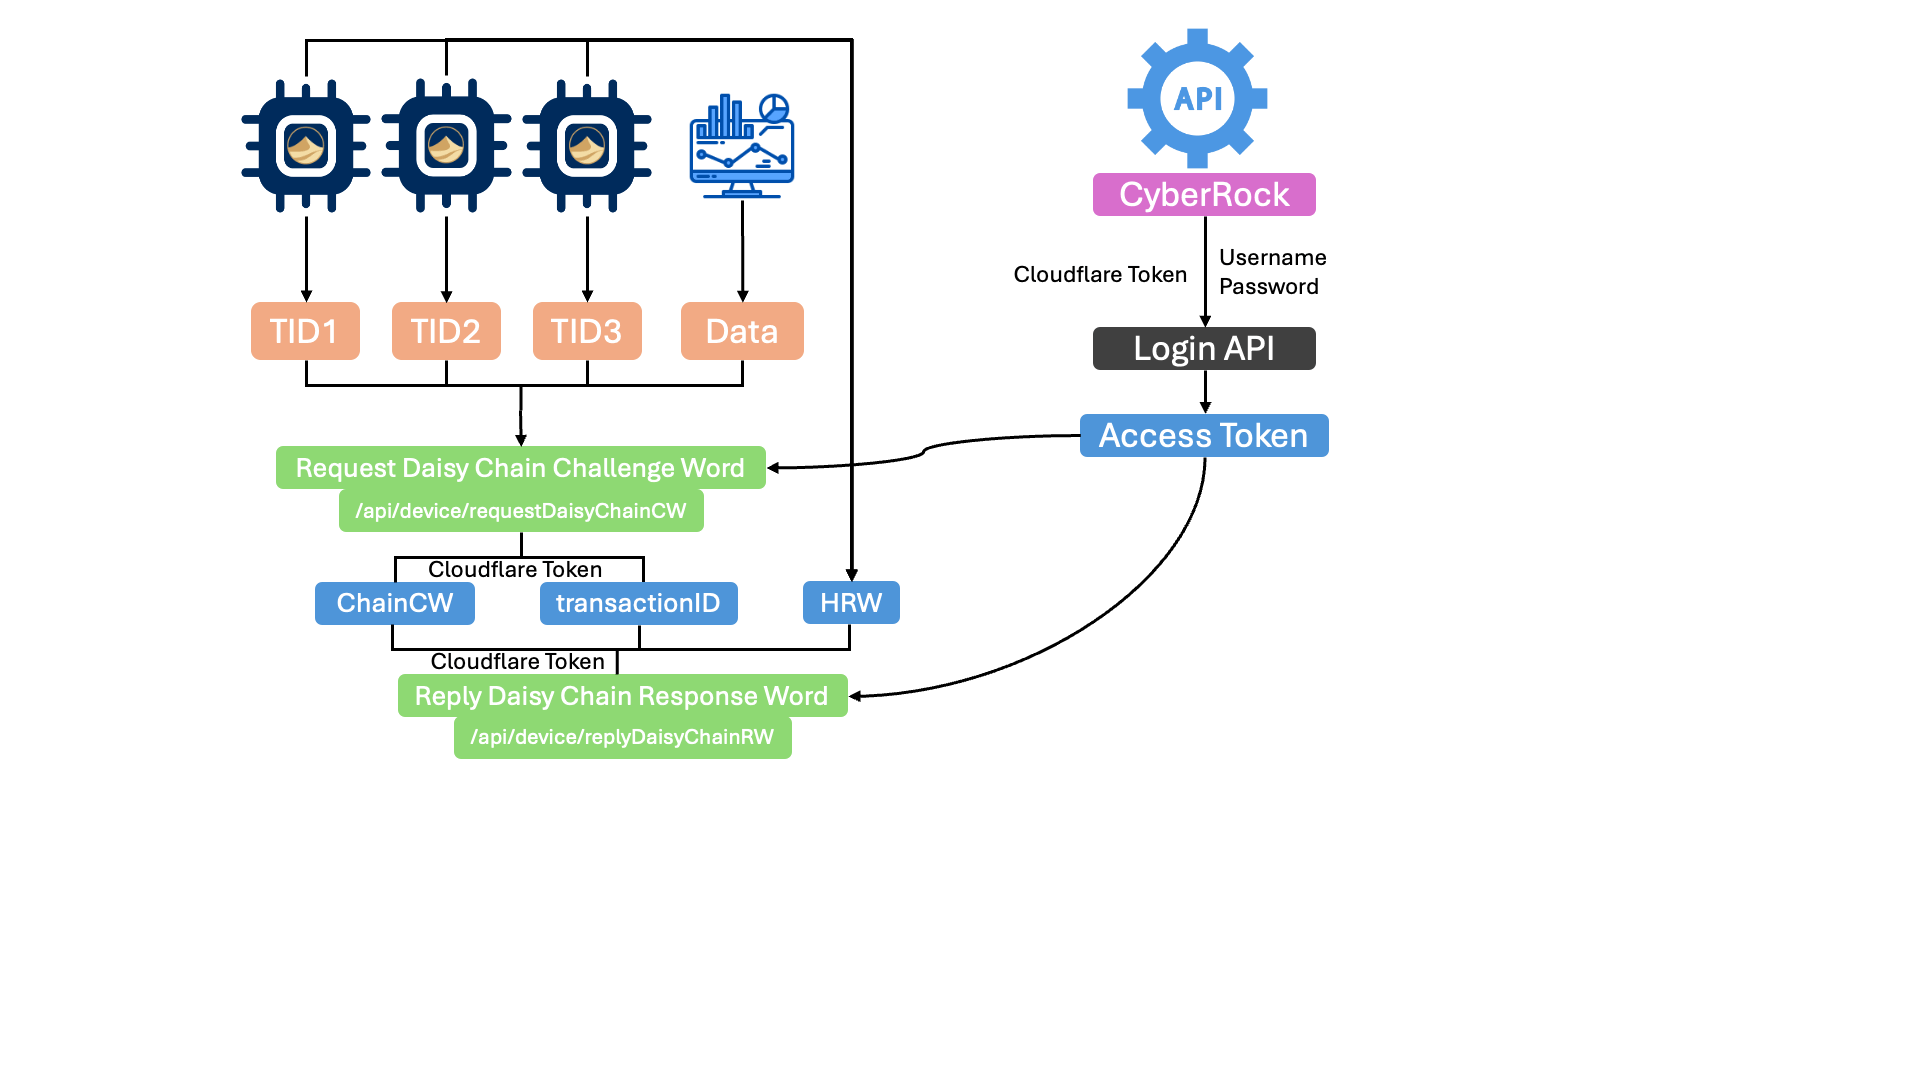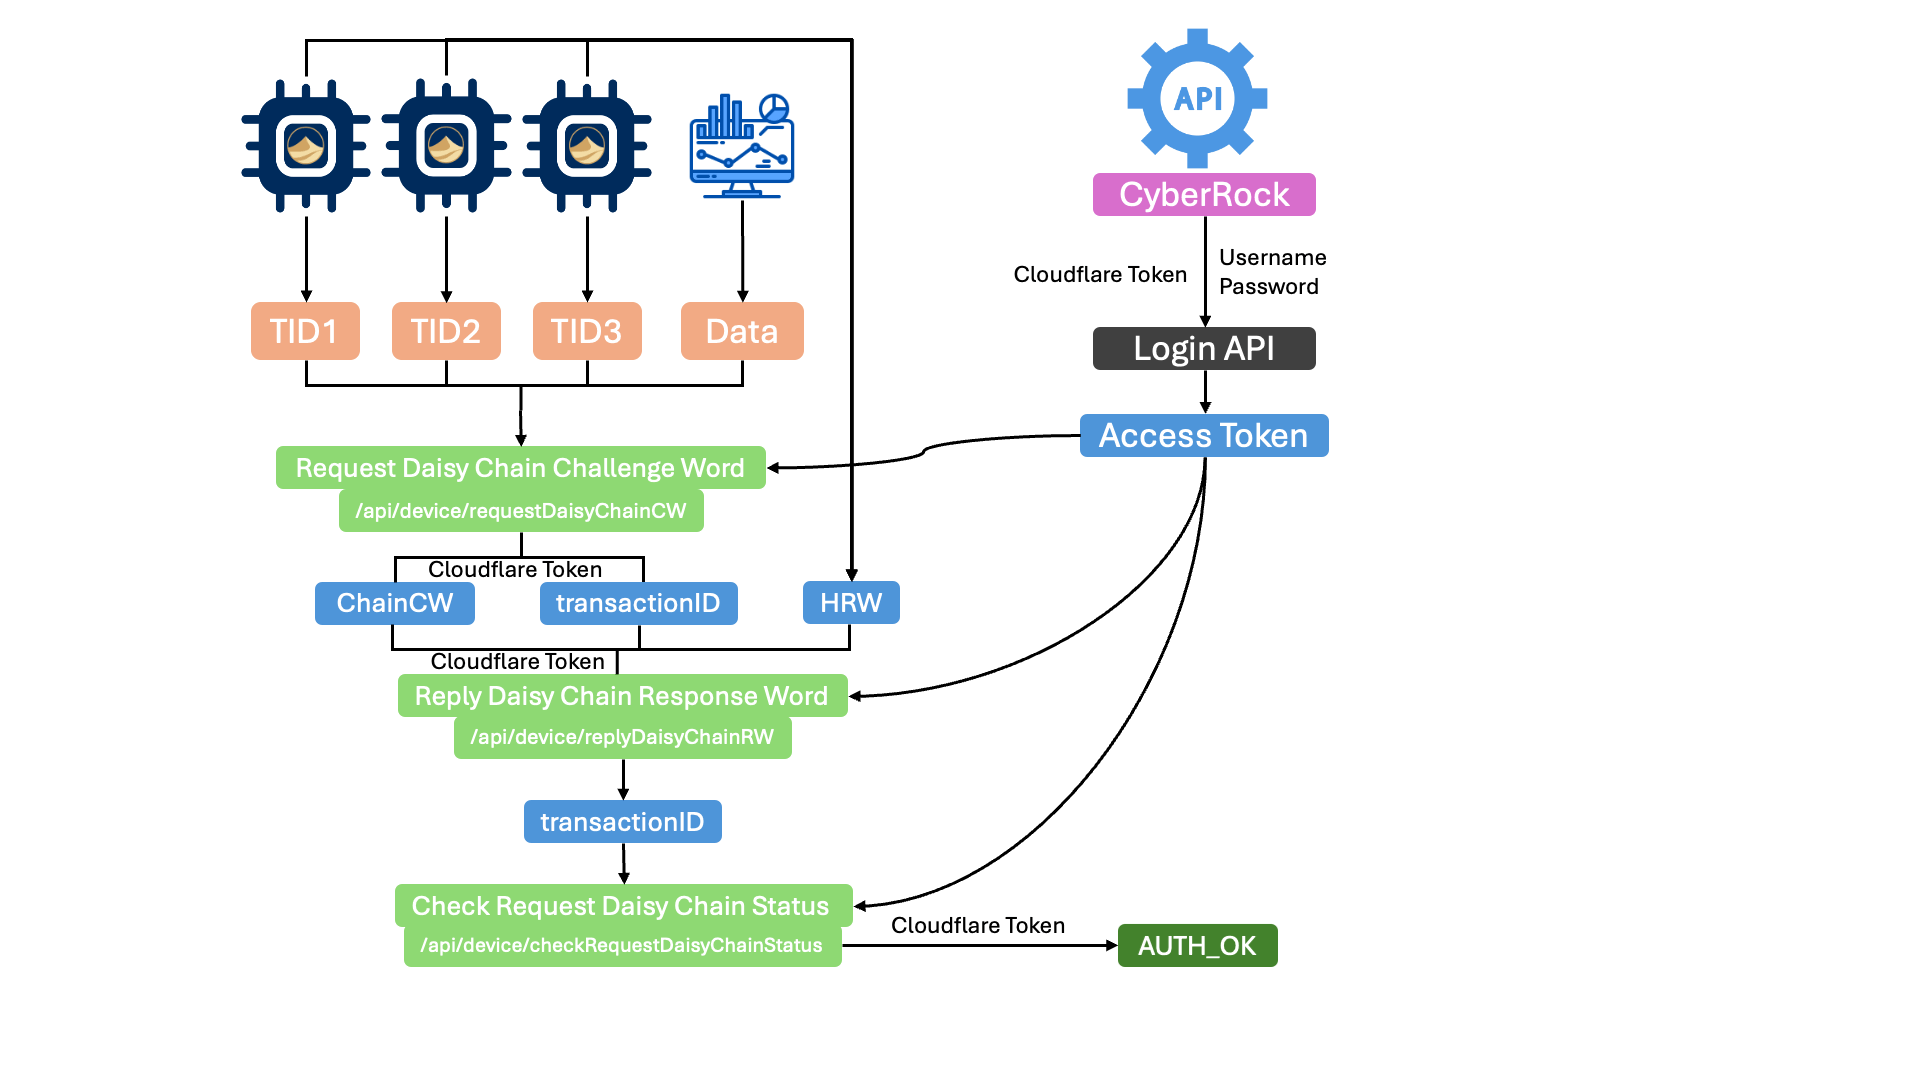
The flow consists of three steps:
- Login Authorization
- Request a Daisy Chain Challenge Word (CW)
- Reply with the Daisy Chain Response Word (RW)
- Check the Daisy Chain Authentication Status
| ← SandGrain Boards | Host Daisy Chain Authentication → |